Enterprise Account Investigation
Correlated failed logons, a later successful sign-in and a privileged group change into one reviewable identity timeline.
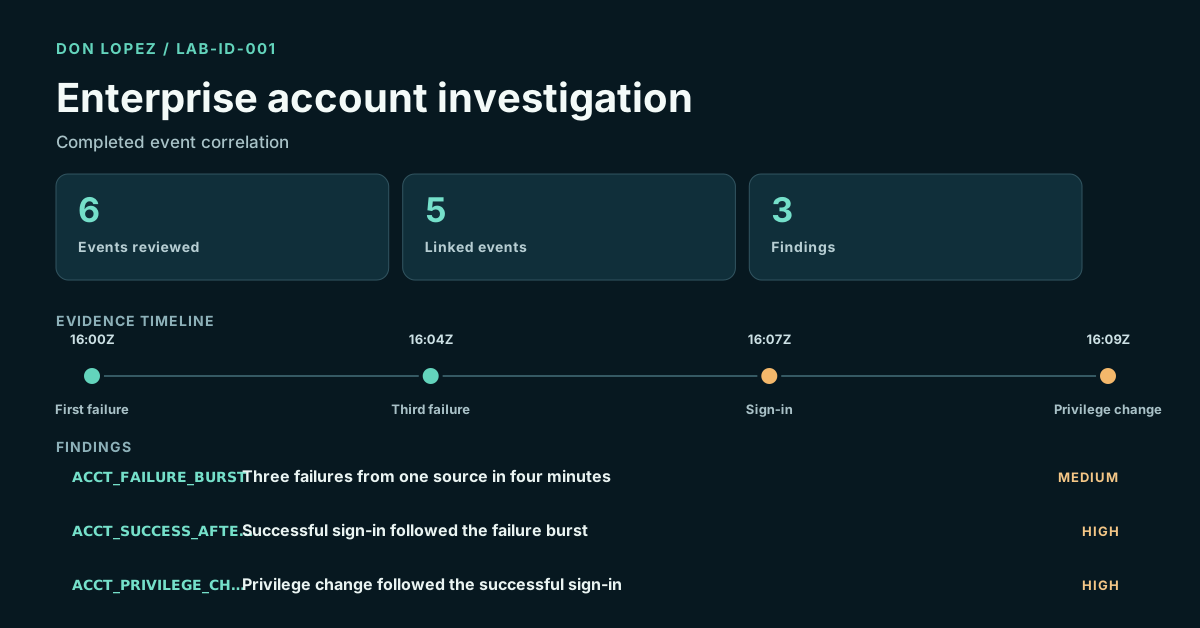
Completed result: five linked account events and three escalation findings.
The investigation question
Did the sequence justify escalation as a linked account event chain? I tested the temporal and identity relationships while keeping alternative administrative explanations visible.
From event to decision
- Bound the failure burst. Three Event 4625 failures occurred for one account and source in four minutes.
- Connected the success. Event 4624 recorded a sign-in from the same source three minutes later.
- Reviewed the privilege change. Event 4728 followed two minutes after the sign-in.
- Kept the conclusion proportionate. The chain warrants escalation, but an approved administrator or automation could explain part of it.
Recommended response
Validate the privileged change, preserve identity and host telemetry, review active sessions and recent account changes, and contain the account if authorization cannot be established.
Inspect the evidence
Academic foundation
Completed coursework: IST 4910 Enterprise Systems Administration and IST 5250 Incident Handling & Cyber Investigation (Fall 2024). Those courses establish the academic context; this current lab supplies its own evidence.
Scope and evidence
The six normalized events are lab-created and use reserved documentation addresses. No real account, domain controller, identity provider, endpoint or production tenant was queried.