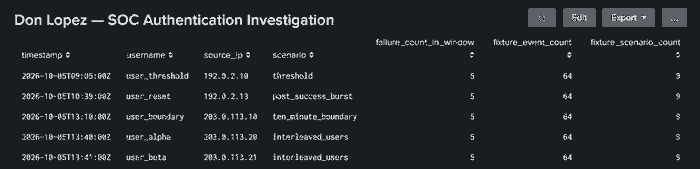
Authentication events → analyst handoff
- Validate
- 70 accepted events · 0 rejected
- Triage
- 6 source-linked review candidates
- Inspect
- Public-safe report excerpt
Synthetic lab data processed through a running Splunk instance.
Splunk Authentication Investigation Workflow
Connected a Splunk authentication export to Python validation, UTC timelines and source-linked reporting. The result is a traceable handoff for SOC investigation—not a claim of confirmed compromise.